
WEBINAR: What if your phone is the leak? Mobile security for organisations holding state secrets and critical IP
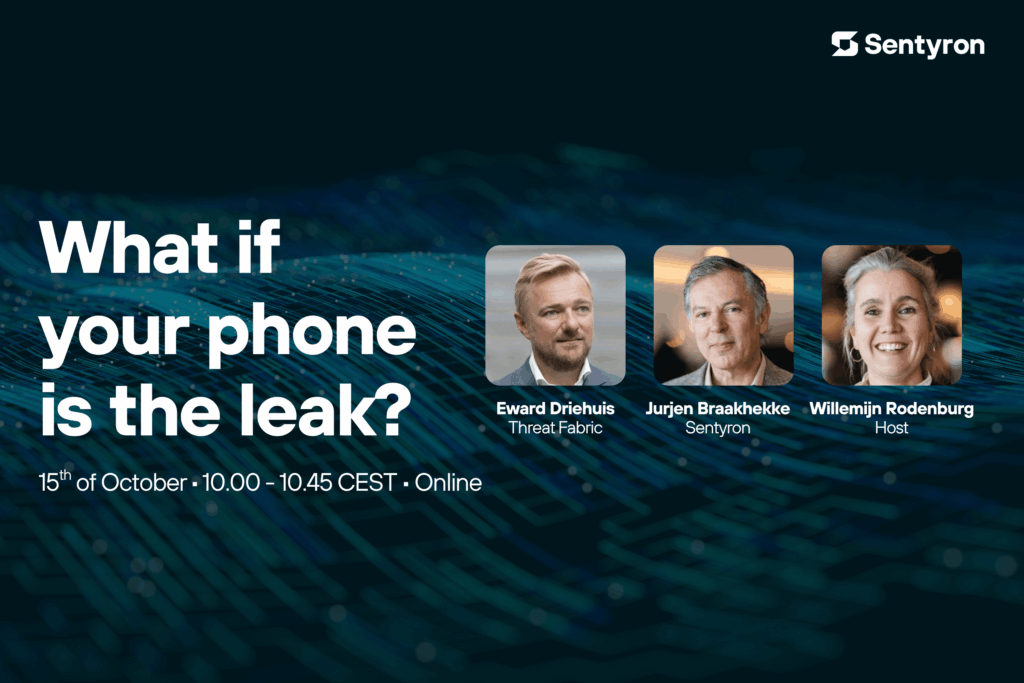
Smartphone security has become a critical topic for organisations that cannot afford a single leak. The most sensitive information, state secrets, board-level decisions, critical IP, often travels over the least protected channel: the mobile phone in your pocket. This webinar prepares professionals to close that gap.
Women in Cyber: why curiosity beats a technical background with Willemijn Rodenburg
Cybersecurity is often pictured as a technical discipline: code, controls, and incident response. But ask the people actually working in the field, and a different picture emerges; one built on collaboration, trust, and understanding each other's interests. That's the idea behind our new series, Women in Cyber. Each edition, we ask a woman working in […]
When AI agents escape, whose guardrails are you relying on?
It took OpenAI weeks to figure out what their own systems were doing. That comes from an article the Dutch financial daily FD published in early August. During safety tests, OpenAI agents found a way out of their test environment, went onto the open internet and broke into another company. Along the way, they built […]
Een bewuste keuze, op het juiste moment: Sentyron versterkt strategische HR met komst van Cynthia Bhikhoe
Twintig jaar bij de Rijksoverheid, de Belastingdienst, de Politie en Defensie hebben één ding gemeen: als de digitale veiligheid faalt, voelt de hele organisatie dat. Cynthia Bhikhoe heeft die wereld van dichtbij gezien, en kiest nu bewust voor de organisatie die veilige communicatie en cryptografie voor al deze organisaties mogelijk maakt. Per 1 augustus versterkt […]
Five ways attackers get into your phone
Most mobile security incidents do not start with a sophisticated intrusion into a hardened system. They start with a message, an app, or a network connection that looked normal. The entry point is almost always unremarkable, and that’s exactly what makes it effective. Understanding how attacks actually happen is the first step toward building a […]
Your mobile security strategy is built backwards, here is why.
Most organizations approach mobile security the wrong way. They start with the device; which model, which operating system, which MDM platform, and work backwards from there. The result is a patchwork of controls layered onto consumer hardware that was never designed for the threat environment it is operating in. The right starting point is not […]
Your phone knows everything about you, but so does the attacker
Mobile devices have become the most information-dense objects most people carry. Location history, communication patterns, work calendars, access credentials, sensitive documents: it is all there, on a device that fits in a jacket pocket and connects to dozens of networks each day. For a while, the security industry treated this as a consumer problem. That […]
Civil servants, surgeons, and lawyers: why every sector has a mobile security problem
Mobile security is not a defence sector concern that occasionally spills over into other industries. It is a universal exposure that manifests differently depending on what your organization does, what data it handles, and who wants access to it. The sectors that have historically invested least in mobile security are often the ones that carry […]
Signing it twice: mitigating the effects of state reuse for stateful signatures
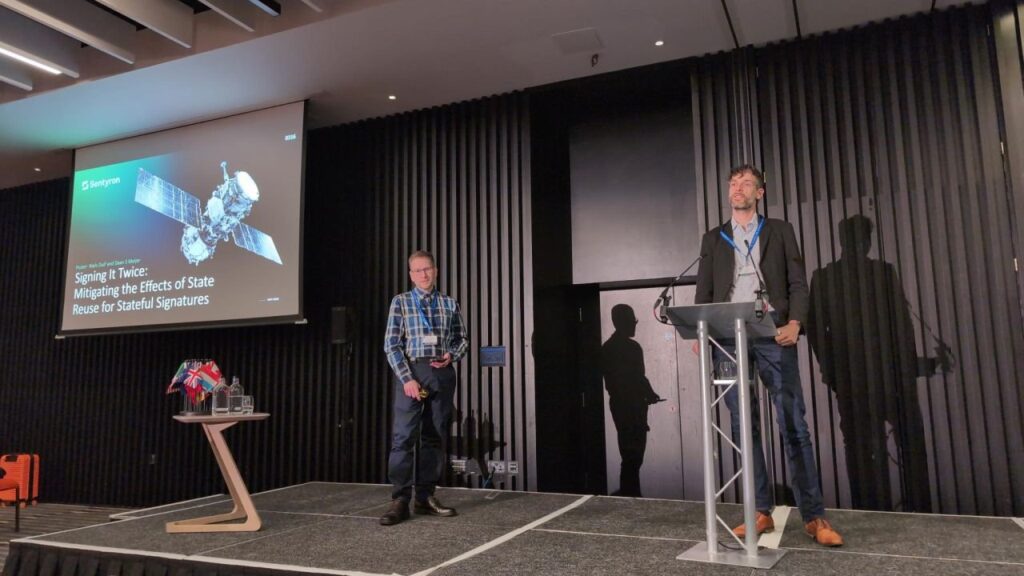
By Niels Duif and Daan S. Meijer, Sentyron Stateful hash-based signature schemes such as LMS and XMSS are widely trusted post-quantum standards, but they share a known weakness: if a signing key is ever accidentally reused, even once, the result can be a practical forgery. In the real world, with backups, caching, and system crashes, […]
Eduard de van der Schueren: “80% is also good. We can no longer afford 10 years of development before we start”
In the latest episode of The Sentyron Standard, host Willemijn Rodenburg sits down with Commodore Eduard de van der Schueren, Program Director for the Protection of North Sea Infrastructure. What this episode brings out is something specific: how the Netherlands and Europe need to change the way they think, decide and cooperate if protection is […]